





Intrinsic transformation: VMware NSX-T and AlgoSec go beyond virtualization


Jeremiah Cornelius, Technical Leader for Alliances and Partners at AlgoSec, explores the security capability native to VMware’s approach for virtual networking with NSX-T.
Intrinsic transformation
NSX-T culminates VMware’s decade of development of these technologies, that better align than ever before with AlgoSec’s approach for software automation of micro-segmentation and compliant security operations management.
It is the latest iteration of VMware’s approach to networking and security, derived from many years as a platform for operating virtual machines, and managing these as hosted “vApp” workloads. If you’re familiar with the main players in Software Defined Networking, then you may remember that NSX-T shares its origin in the same student research at Stanford University, which also gave rise to several other competing SDN offerings.
One thing that differentiated VMware from other players was their strong focus on virtualization over traditional network equipment stacks. This meant in some cases, network connections, data-packets, forwarding, and endpoints all existing in software and no “copper wire” existing anywhere! Knowing about this difference is more than a bit of trivia — it explains how the NSX family was designed with security features built into the architecture, having native capability for software security controls such as firewall segmentation and packet inspection. Described by VMware as “Intrinsic Security,” these are NSX capabilities that first drove the widespread acceptance of practical micro-segmentation in the data center.
Since that first introduction of NSX micro-segmentation, a transformation occurred in customer demands, which required an expansion of VMware’s universe to horizons beyond their hypervisor and virtual machines. As a key enabler for this expansion, NSX-T has emerged as a networking and security technology that extends from serverless micro-services and container frameworks to VMs hosted on many cloud architectures located in physical data centers or as tenants in public clouds. The current iteration is called the NSX-T Service-Defined Firewall, which controls access to applications and services along with business-focused policies.
Leaders in our segments
If you’ve followed this far along, then maybe you’ve recognized several common themes between AlgoSec’s Security Management Suite and VMware’s NSX-T. Among these are security operations management as software configuration, modeling connectivity on business uses versus technology conventions, and transforming security into an enabling function. It’s not a surprise then, to know that our companies are technology partners.
In fact, we began our alliance with VMware back in 2015 as the uptake in NSX micro-segmentation began to reveal an increased need for visibility, planning, automation, and reporting — along with requirements for extending policy from NSX objects to attached physical security devices from a variety of vendors.
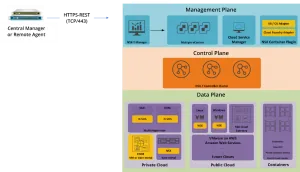
The sophistication and flexibility of NSX enforcement capability were excellently matched by the AlgoSec strengths in identifying risk and maintaining compliance while sustaining a change management record of configurations from our combined workflow automation.
Strength to strength
Up until now, this is a rosy picture painted, with an emphasis on the upsides of the AlgoSec partnership with VMware NSX-T. In the real world, we find that many of our applications are not-so-well understood as to be ready for micro-segmentation. More often, the teams responsible for the availability and security of these applications are detached from the business intent and value, further making it difficult to assess and therefore address risks. The line between traditional-style infrastructure and modern services isn’t always as clearly defined, either — making the advantages possible by migration and transformation difficult to determine and potentially introducing their own risks. It is in these environments, with multiple technologies, different stakeholders, and operation teams with different scopes, that AlgoSec solves hard problems with better automation tools.
Taking advantage of NSX-T means first being faced with multiple deployment types, including public and private clouds as well as on-prem infrastructure, multiple security vendors, unclear existing network flows, and missing associations between business applications and their existing controls. These are visibility issues that AlgoSec resolves by automating the discovery and mapping of business applications, including associated policies across different technologies, and producing visual, graphic analysis that includes risk assessment and impact of changes.
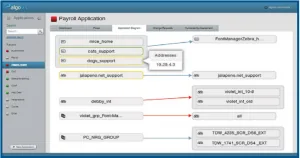
This capability for full visibility leads directly to addressing the open issues for risk and compliance. After all, if these present challenges in discovering and identifying risk using existing technology solutions, then there’s a big gap to close on the way to transforming these. Since AlgoSec has addressed the visibility across these, identifying risk becomes uniform and manageable. AlgoSec can lower transformation risk with NSX-T while ensuring that risk and compliance management are maintained on an ongoing basis. Workflow for risk mitigation by NSX-T intrinsic security can be driven by AlgoSec policy automation, without recourse to multiple tools when these mitigations need to cross boundaries to third-party firewalls or cloud security controls. With this integrated policy automation, what were once point-in-time configurations can be enabled for discovery-based updates for internal standards and changes to regulatory mandates.
The result of AlgoSec pairing with VMWare NSX-T is a simplified overall security architecture — one that more rapidly responds to emerging risk and requests for changes, accelerates the speed of operations while more closely aligning with business, and ensures both compliant configurations and compliant lifecycle operations.
VMware NSX? Ask AlgoSec
The AlgoSec integration with VMware NSX-T builds on our years of collaboration with earlier versions of the NSX platform, with a track record of solving the more difficult configuration management problems for leaders of principal industries around the globe.
If you want to discover more about what AlgoSec does to enable and enrich our alliance solution with VMware, contact us! AlgoSec works directly with VMware and your trusted technology delivery partners, and we’re glad to share more with you. Schedule a personal demo to see how AlgoSec makes your transformation to VMware Intrinsic Security possible now.
Jeremiah Cornelius
Jeremiah Cornelius es el líder técnico de alianzas y socios en AlgoSec, donde aporta liderazgo técnico en las relaciones de alianza con sus socios de red y seguridad. Es un profesional de la seguridad de la información desde 1995 y anteriormente fue arquitecto de seguridad y especialista en tecnología en líderes de la industria como Microsoft y VMware.