Financial institutions are dealing with the triple challenge of digital transformation, cyber security and regulations. They are constantly seeking to better serve their customers and establish a competitive edge through new technology innovations. But all too often, they fall behind on delivering these digital initiatives into production. Why does this happen? Network security operations teams are hampered by manual, slow and error-prone security change-management processes and the ever-increasing demands of industry regulations. Often requiring days, or even weeks, to process a single change across their complex network environment, security teams are deluged with hundreds of changes each month, hindering time-to-market. Security teams fight hard to create and maintain a clean and optimized network security policy that reduces the attack surface. But the frequent errors that arise from manual processes put the institution at cyber risk, opening security gaps that attract unwanted elements. Errors also introduce regulation-compliance gaps. Financial institutions find themselves struggling with the next audit instead of passing with flying colors.
AlgoSec’s unique, business-driven approach to security management enables financial institutions to align security policy management with their business initiatives and processes, making them more agile, more secure and more compliant all the time.
Supporting DORA Compliance with AlgoSec
The Digital Operational Resilience Act (DORA) places greater emphasis on ICT risk management, operational resilience, and effective security controls across financial institutions. AlgoSec helps organizations support these requirements by providing visibility into application connectivity, automating security policy changes, and identifying risky or unnecessary network security rules. Through rule recertification (also known as rule attestation), organizations can periodically validate whether existing security policy rules remain necessary, reduce excessive access, and maintain documented evidence to support security reviews and regulatory audits.
With AlgoSec you can
- Automate the entire security policy management process – with zero-touch
- Manage the entire enterprise environment through a single pane of glass
- Proactively assess the risk of every change before it is implemented
- Automatically identify and remove bloat and clutter from security policies
- Automate firewall auditing and ensure continuous compliance
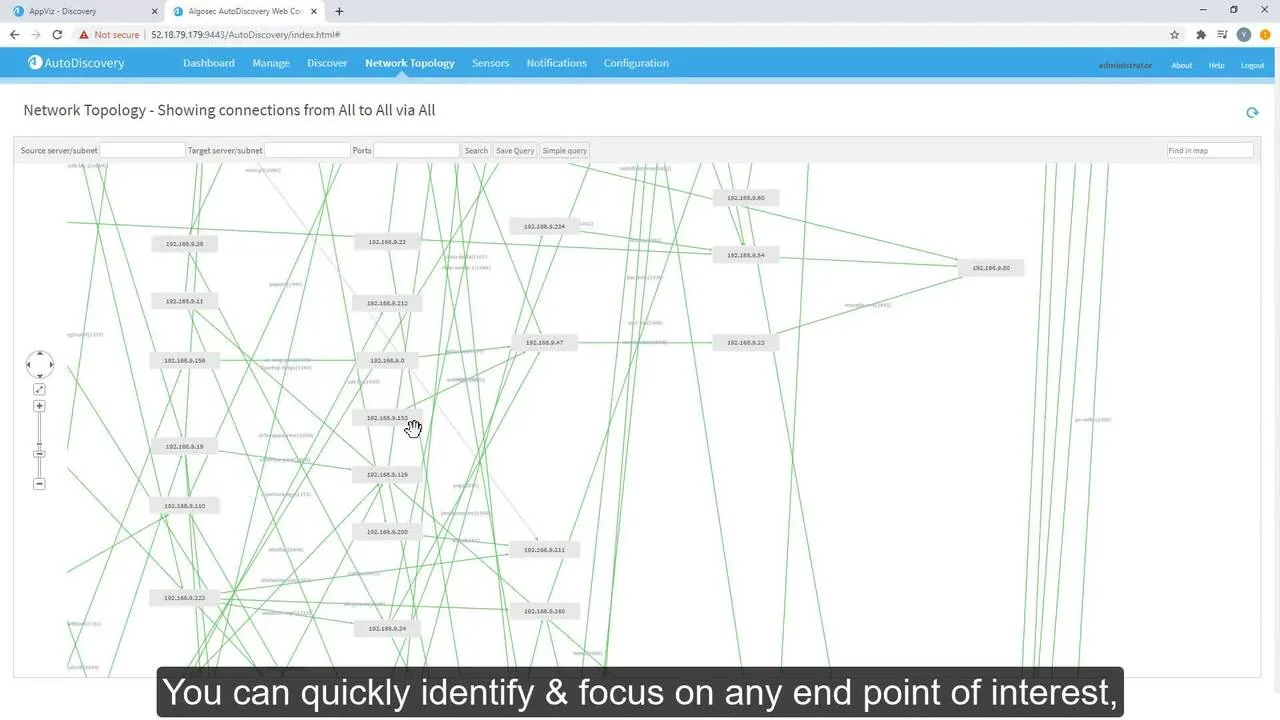
- Automatically discover, map and migrate application connectivity through easy-to-use workflows
- Support DORA-related ICT risk management through network security rule recertification (rule attestation), security policy optimization, and audit-ready documentation.
The business impact
- Get consistent, unified security management across any heterogeneous network environment
- Deploy applications faster by automating network security change management processes
- Avoid security device misconfigurations that cause outages
- Migrate application connectivity to the cloud quickly and easily
- Ensure a clean and optimized security policy
- Reduce the costs and efforts of firewall auditing and ensure continuous compliance
- Facilitate effective communication between security teams and application owners
FAQ
How can banks accelerate application delivery while controlling network security risk?

AlgoSec helps financial institutions proactively assess the risk of network security changes before implementation and automate security policy change management. It also discovers and maps application connectivity, enabling faster application deployment and migration while helping avoid misconfigurations that can cause outages.
How does AlgoSec support DORA-related network security governance for financial institutions?
AlgoSec supports financial institutions with centralized security policy visibility, proactive risk assessment, automated firewall auditing, and continuous compliance reporting. These capabilities can contribute evidence and technical controls relevant to DORA ICT risk management. They can also inform periodic firewall rule recertification (rule attestation), although DORA does not prescribe that specific process by name and AlgoSec alone does not guarantee regulatory compliance.
How can financial institutions simplify firewall audits and security policy cleanup?
AlgoSec helps financial institutions identify and remove unnecessary security policy bloat, automate firewall auditing, and manage heterogeneous networks through a centralized view. It also supports communication between security teams and application owners, helping organizations maintain cleaner policies and reduce the effort required for recurring audits.
What is FireFlow?
FireFlow automates the security change policy process from planning through deployment to production. FireFlow integrates with your existing with IT Service Management (ITSM) solutions, such as ServiceNow, BMC Remedy and HP for quick, accurate changes.
How can I manage my firewall security policy?
Answer text goes here.
How can I manage my firewall's inbound & outbound rules?
Answer text goes here.
What are firewall change requests?
Answer text goes here.
What are firewall policy rules?
Answer text goes here.
What are the best practices for managing firewall policy rules?
Answer text goes here.