




Videos
Explore all our videos
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.


Filters
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.

Showing 0 results
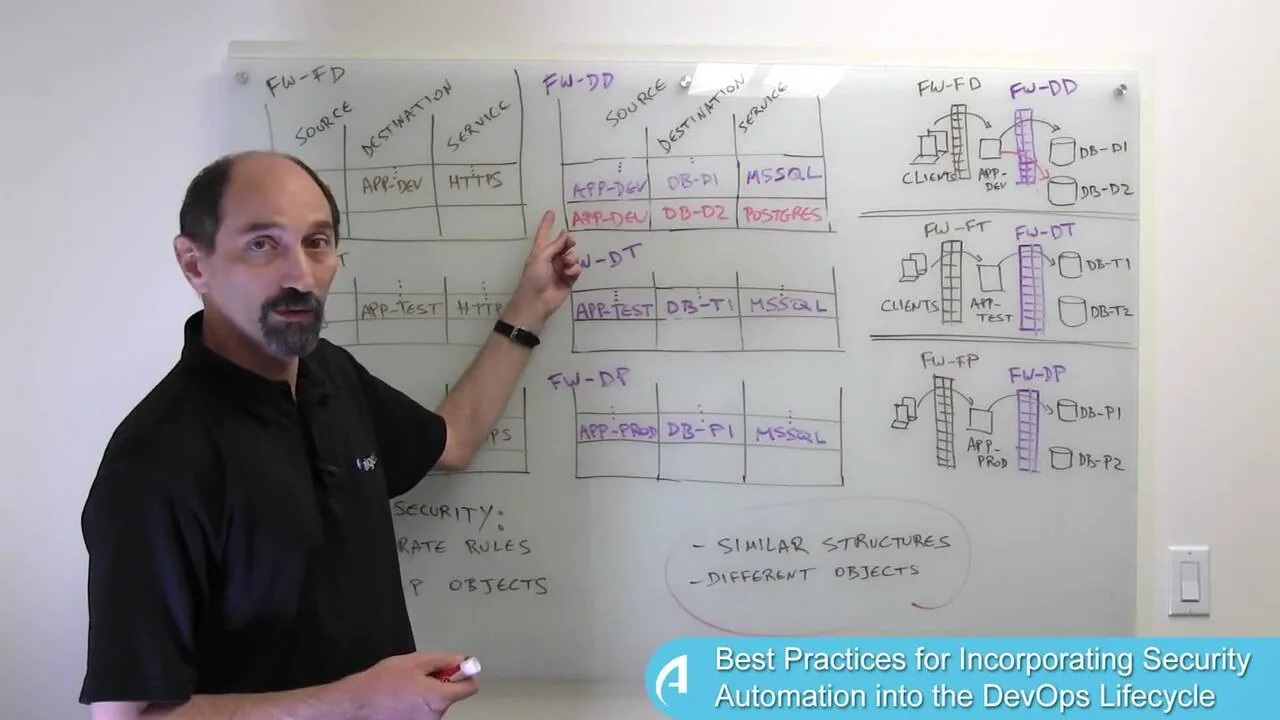
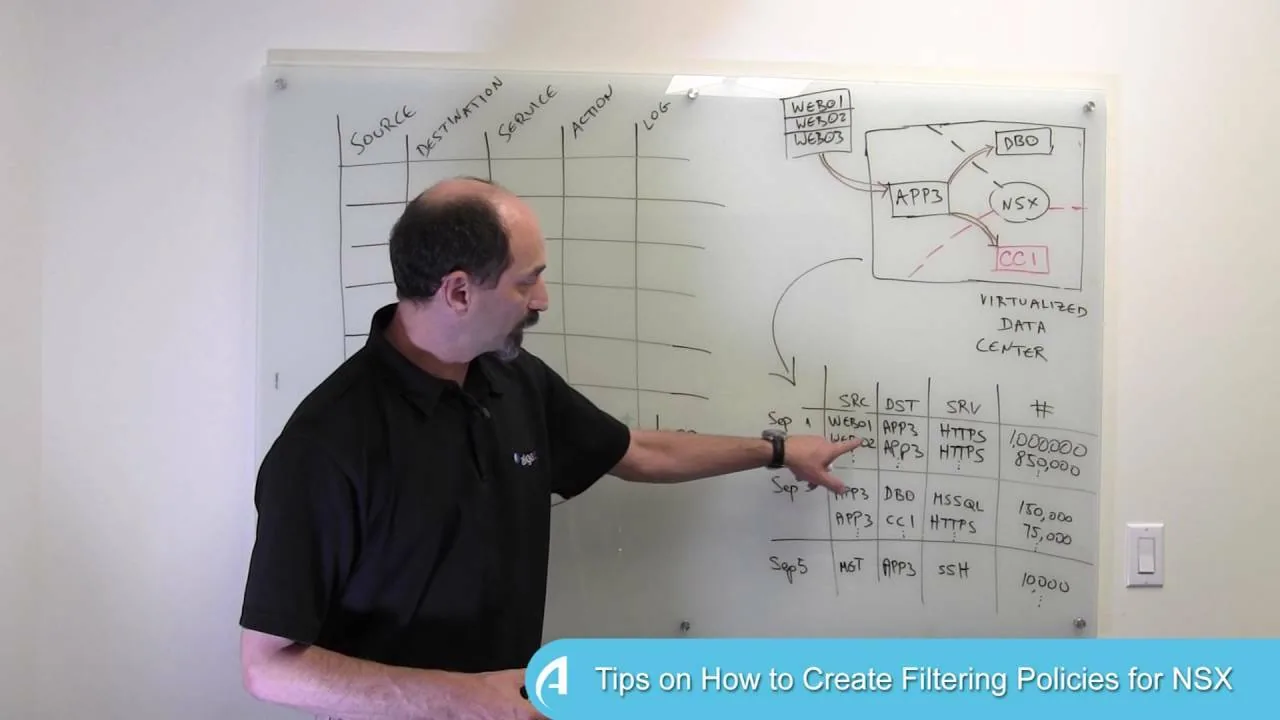


Lesson 2: Tips on how to create filtering policies for NSX
Network Security for VMware NSX: Lesson 2 When setting up an NSX data center you need to write filtering policies for any traffic that goes into an NSX data center, exits from it, or moves between different servers inside the NSX data center. In this lesson, Professor Wool recommends a multi-stage process to help users write secure and effective policies for east East-West traffic. Learn more about AlgoSec at http://www.algosec.com and read Professor Wool's blog posts athttps://www.algosec.com/blog
Watch

Application connectivity management
Professor Wool
Connectivity management
Hybrid cloud security management
Network segmentation
Security policy management
Solution partners
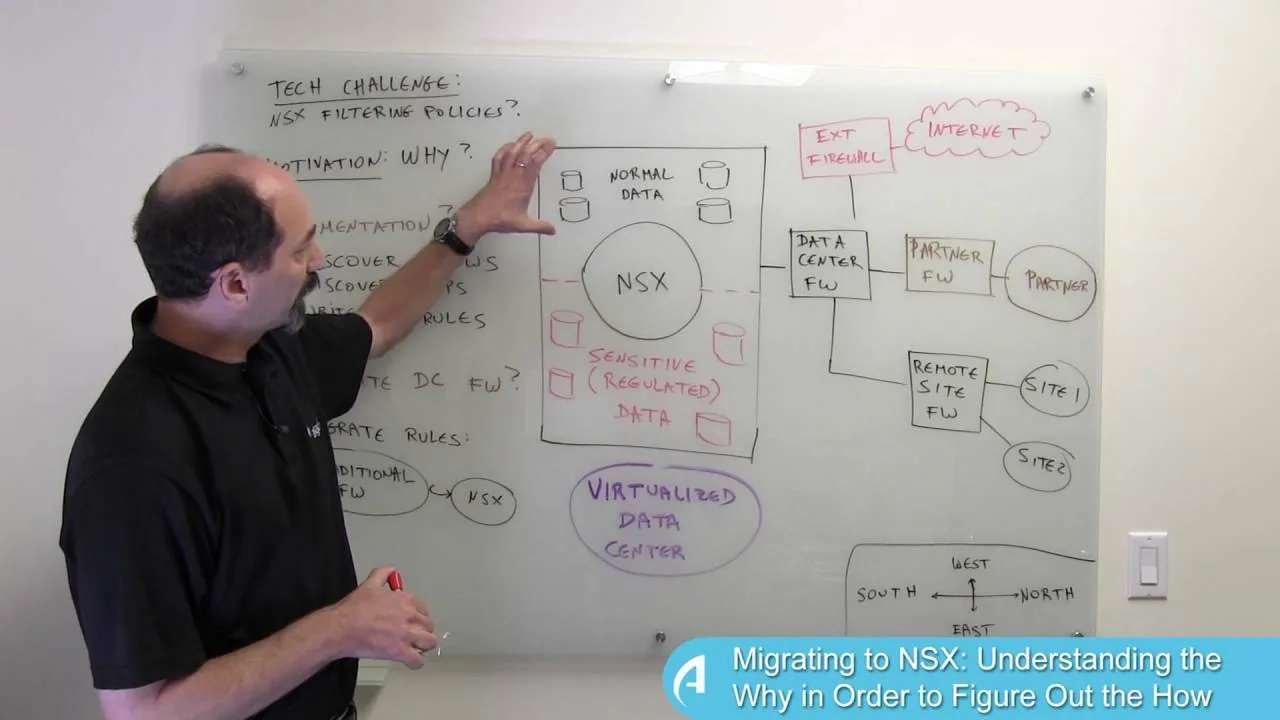
Lesson 1: Migrating to NSX: Understanding the why in order to figure out the how
VMware’s NSX enables datacenter owners to secure East-West traffic using filtering policies that are enforced by the VMware infrastructure. However, migrating from existing traditional filtering technologies to VMware NSX can be a daunting task. In this lesson Professor will discuss why it’s important to understand the motivations for a migration to NSX in order to successfully plan and implement the actual migration to the VMware NSX platform. Learn more about AlgoSec at http://www.algosec.com and read Professor Wool's blog posts athttps://www.algosec.com/blog
Watch
Application connectivity management
Professor Wool
Connectivity management
Hybrid cloud security management
Network segmentation
Security policy management
Solution partners
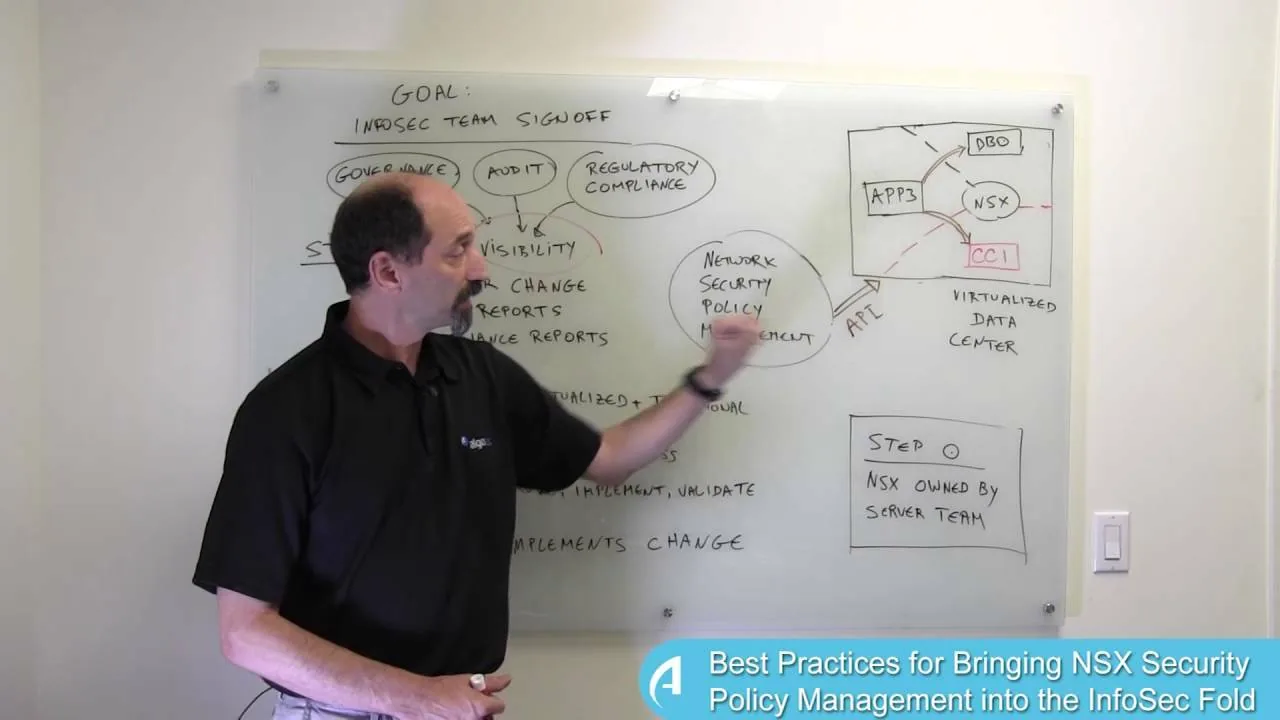
Lesson 3: Best practices for bringing NSX security policy management into the InfoSec fold
Network Security for VMware NSX: Lesson 3 Once the NSX environment is up and running it needs to be part of the organization’s network security policy change process, and subject to the organization’s governance, audit, and regulatory compliance requirements. In this lesson Professor Wool discusses how to approach managing changes, auditing and compliance when the security team doesn’t ‘own’ the virtual environment.
Watch
Application connectivity management
Professor Wool
Auditing and compliance
Connectivity management
Hybrid cloud security management
Network segmentation
Security policy management
Solution partners
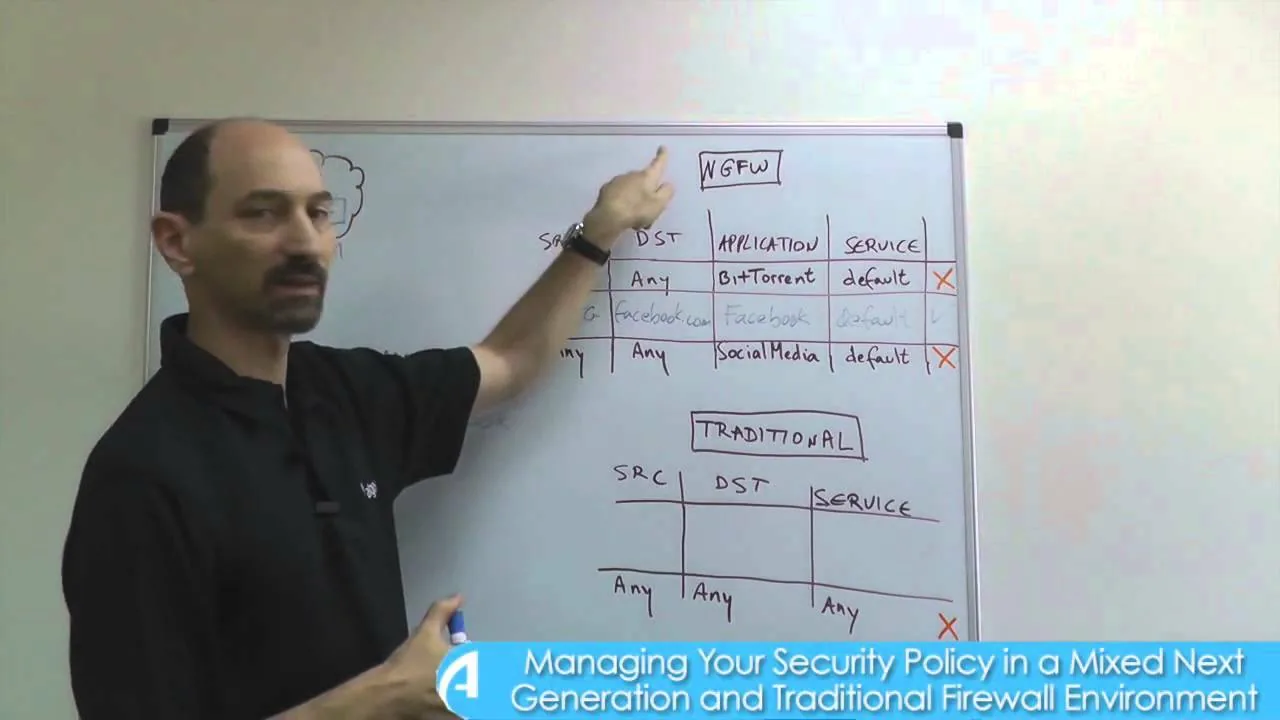
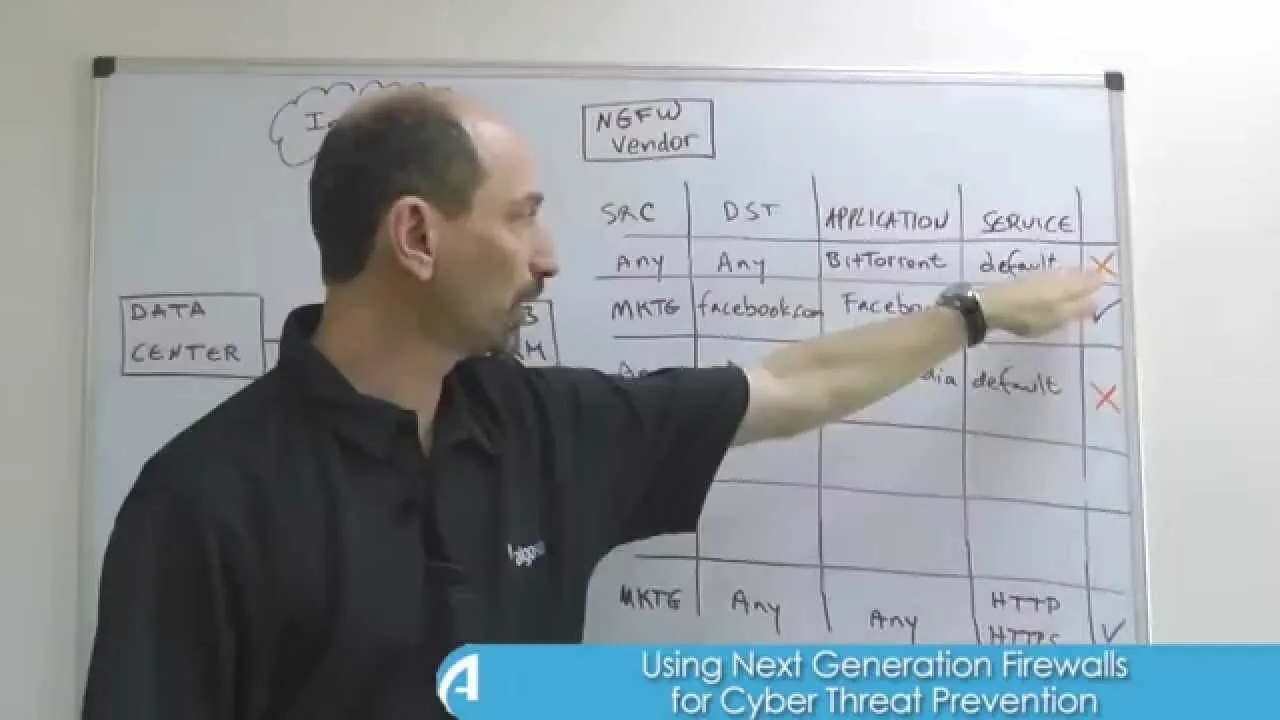
Lesson 4: Using next generation firewalls for cyber threat prevention
Next Generation Firewalls: Lesson 4 As part of the blacklisting approach to application security, most NGFW vendors now offer their customers a subscription based service that provides periodic updates to firewall definitions and signatures for a great number of applications especially the malicious ones. In this lesson, Professor Wool discusses the pros and cons of this offering for cyber threat prevention. It also discusses the limitations of this service when home-grown applications are deployed in the enterprise, and provides a recommendation on how to solve this problem. Learn more about AlgoSec at http://www.algosec.com and read Professor Wool's blog posts at https://www.algosec.com/blog
Watch
Cyber attacks & incident response
Firewall change management
Professor Wool
Network security
Security policy management
No results found