





Your complete guide to cloud security architecture


In today’s digital world, is your data 100% secure?
As more people and businesses use cloud services to handle their data, vulnerabilities multiply. Around six out of ten companies have moved to the cloud, according to Statista. So keeping data safe is now a crucial concern for most large companies – in 2022, the average data leak cost companies $4.35 million.
This is where cloud security architecture comes in.
Done well, it protects cloud-based data from hackers, leaks, and other online threats. To give you a thorough understanding of cloud security architecture, we’ll look at;
- What cloud security architecture is
- The top risks for your cloud
- How to build your cloud security
- How to choose a CPSM (Cloud Security Posture Management) tool
Let’s jump in
What is cloud security architecture?
Let’s start with a definition:
“Cloud security architecture is the umbrella term used to describe all hardware, software and infrastructure that protects the cloud environment and its components, such as data, workloads, containers, virtual machines and APIs.” (source)
Cloud security architecture is a framework to protect data stored or used in the cloud. It includes ways to keep data safe, such as controlling access, encrypting sensitive information, and ensuring the network is secure. The framework has to be comprehensive because the cloud can be vulnerable to different types of attacks.
Three key principles behind cloud security
Although cloud security sounds complex, it can be broken down into three key ideas. These are known as the ‘CIA triad’, and they are;
- Confidentiality
- Integrity
- Availability
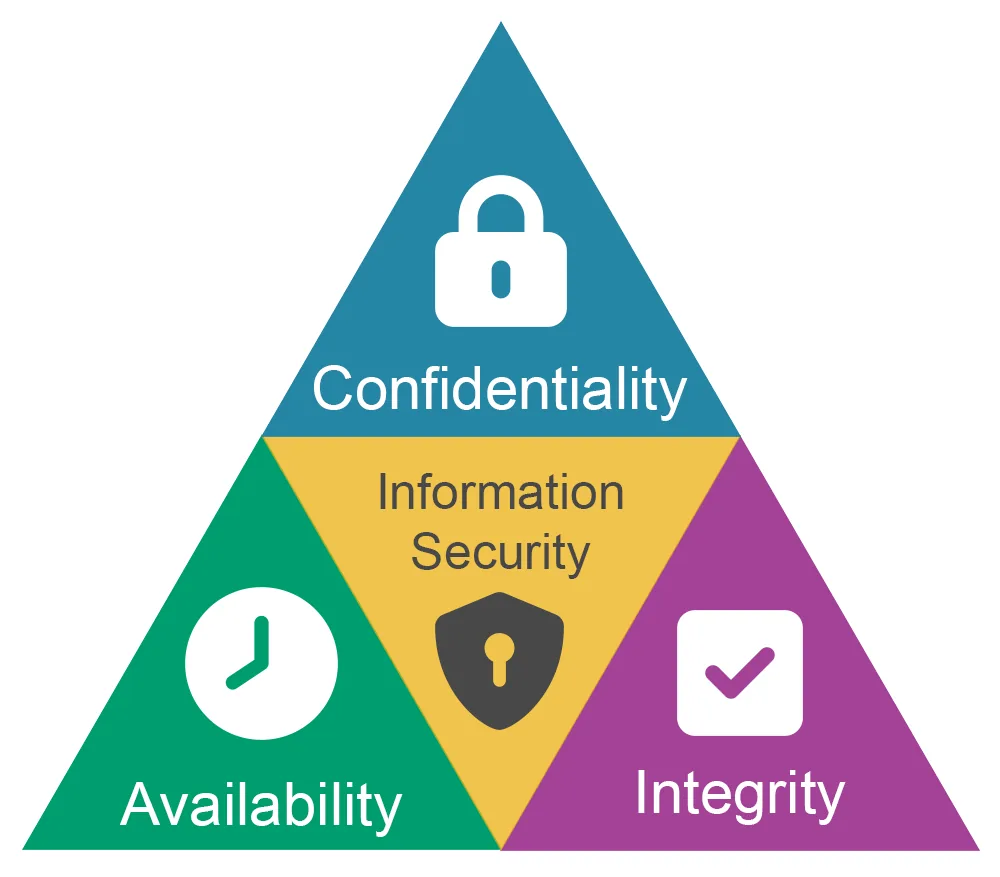
‘The CIA Triad’ Image source
Confidentiality
Confidentiality is concerned with data protection. If only the correct people can access important information, breaches will be reduced. There are many ways to do this, like encryption, access control, and user authentication.
Integrity
Integrity means making sure data stays accurate throughout its lifecycle. Organizations can use checksums and digital signatures to ensure that data doesn’t get changed or deleted. These protect against data corruption and make sure that information stays reliable.
Availability
Availability is about ensuring data and resources are available when people need them. To do this, you need a robust infrastructure and ways to switch to backup systems when required.
Availability also means designing systems that can handle ‘dos attacks’ and will interrupt service.
However, these three principles are just the start of a strong cloud infrastructure. The next step is for the cloud provider and customer to understand their security responsibilities.
A model developed to do this is called the ‘Shared Responsibility Model.’
Understanding the shared responsibility model
Big companies like Amazon Web Services (AWS), Microsoft Azure, and Google Cloud Platform offer public cloud services. These companies have a culture of being security-minded, but security isn’t their responsibility alone.
Companies that use these services also share responsibility for handling data. The division of responsibility depends on the service model a customer chooses. This division led Amazon AWS to create a ‘shared responsibility model’ that outlines these.
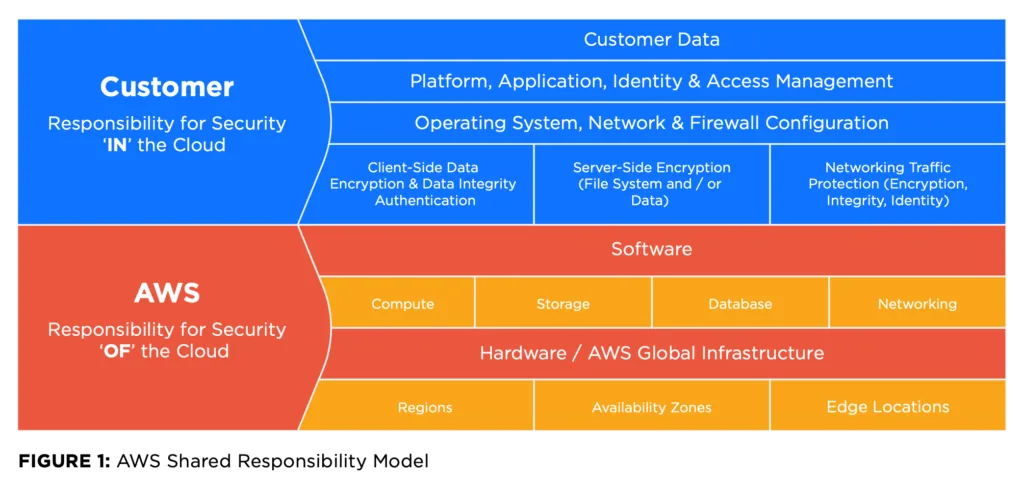
There are three main kinds of cloud service models and associated duties:
1. Infrastructure as a Service (IaaS),
2. Platform as a Service (PaaS)
3. Software as a Service (SaaS).
Each type gives different levels of control and flexibility.
1. Infrastructure as a Service (IaaS)
With IaaS, the provider gives users virtual servers, storage, and networking resources. Users control operating systems, but the provider manages the basic infrastructure. Customers must have good security measures, like access controls and data encryption. They also need to handle software updates and security patches.
2. Platform as a Service (PaaS)
PaaS lets users create and run apps without worrying about having hardware on-premises. The provider handles infrastructure like servers, storage, and networking. Customers still need to control access and keep data safe.
3. Software as a Service (SaaS)
SaaS lets users access apps without having to manage any software themselves. The provider handles everything, like updates, security, and basic infrastructure. Users can access the software through their browser and start using it immediately. But customers still need to manage their data and ensure secure access.
Top six cybersecurity risks
As more companies move their data and apps to the cloud, there are more chances for security to occur. Although cybersecurity risks change over time, some common cloud security risks are:
1. Human error
99% of all cloud security incidents from now until 2025 are expected to result from human error. Errors can be minor, like using weak passwords or accidentally sharing sensitive information. They can also be bigger, like setting up security incorrectly. To lower the risk of human error, organizations can take several actions. For example, educating employees, using automation, and having good change management procedures.
2. Denial-of-service attacks
DoS attacks stop a service from working by sending too many requests. This can make essential apps, data, and resources unavailable in the cloud. DDoS attacks are more advanced than DoS attacks, and can be very destructive. To protect against these attacks, organizations should use cloud-based DDoS protection. They can also install firewalls and intrusion prevention systems to secure cloud resources.
3. Hardware strength
The strength of the physical hardware used for cloud services is critical. Companies should look carefully at their cloud service providers (CSPs) hardware offering. Users can also use special devices called hardware security modules (HSMs). These are used to protect encryption codes and ensure data security.
4. Insider attacks
Insider attacks could be led by current or former employees, or key service providers. These are incredibly expensive, costing companies $15.38 million on average in 2021. To stop these attacks, organizations should have strict access control policies. These could include checking access regularly and watching for strange user behavior. They should also only give users access to what they need for their job.
5. Shadow IT
Shadow IT is when people use unauthorized apps, devices, or services. Easy-to-use cloud services are an obvious cause of shadow IT. This can lead to data breaches, compliance issues, and security problems. Organizations should have clear rules about using cloud services. All policies should be run through a centralized IT control to handle this.
6. Cloud edge
When we process data closer to us, rather than in a data center, we refer to the data as being in the cloud edge. The issue? The cloud edge can be attacked more easily. There are simply more places to attack, and sensitive data might be stored in less secure spots. Companies should ensure security policies cover edge devices and networks. They should encrypt all data, and use the latest application security patches.
Six steps to secure your cloud
Now we know the biggest security risks, we can look at how to secure our cloud architecture against them.
An important aspect of cloud security practices is managing access your cloud resources. Deciding who can access and what they can do can make a crucial difference to security. Identity and Access Management (IAM) security models can help with this. Companies can do this by controlling user access based on roles and responsibilities. Security requirements of IAM include:
1. Authentication
Authentication is simply checking user identity when they access your data. At a superficial level, this means asking for a username and password. More advanced methods include multi-factor authentication for apps or user segmentation. Multi-factor authentication requires users to provide two or more types of proof.
2. Authorization
Authorization means allowing access to resources based on user roles and permissions. This ensures that users can only use the data and services they need for their job. Limiting access reduces the risk of unauthorized users. Role-based access control (RBAC) is one way to do this in a cloud environment. This is where users are granted access based on their job roles.
3. Auditing
Auditing involves monitoring and recording user activities in a cloud environment. This helps find possible security problems and keeps an access log. Organizations can identify unusual patterns or suspicious behavior by regularly reviewing access logs.
4. Encryption at rest and in transit
Data at rest is data when it’s not being used, and data in transit is data being sent between devices or users. Encryption is a way to protect data from unauthorized access. This is done by converting it into a code that can only be read by someone with the right key to unlock it. When data is stored in the cloud, it’s important to encrypt it to protect it from prying eyes. Many cloud service providers have built-in encryption features for data at rest.
For data in transit, encryption methods like SSL/TLS help prevent interception. This ensures that sensitive information remains secure as it moves across networks.
5. Network security and firewalls
Good network security controls are essential for keeping a cloud environment safe. One of the key network security measures is using firewalls to control traffic. Firewalls are gatekeepers, blocking certain types of connections based on rules.
Intrusion detection and prevention systems (IDPS) are another important network security tool. IDPS tools watch network traffic for signs of bad activity, like hacking or malware. They then can automatically block or alert administrators about potential threats. This helps organizations respond quickly to security incidents and minimize damage.
6. Versioning and logging
Versioning is tracking different versions of cloud resources, like apps and data. This allows companies to roll back to a previous version in case of a security incident or data breach. By maintaining a version history, organizations can identify and address security vulnerabilities.
How a CSPM can help protect your cloud security
A Cloud Security Posture Management (CSPM) tool helpful to safeguard cloud security. These security tools monitor your cloud environment to find and fix potential problems. Selecting the right one is essential for maintaining the security of your cloud.
A CSPM tool like Prevasio management service can help you and your cloud environment. It can provide alerts, notifying you of any concerns with security policies. This allows you to address problems quickly and efficiently.
Here are some of the features that Prevasio offers:
- Agentless CSPM solution
- Secure multi-cloud environments within 3 minutes
- Coverage across multi-cloud, multi-accounts, cloud-native services, and cloud applications
- Prioritized risk list based on CIS benchmarks
- Uncover hidden backdoors in container environments
- Identify misconfigurations and security threats
- Dynamic behavior analysis for container security issues
- Static analysis for container vulnerabilities and malware
All these allow you to fix information security issues quickly to avoid data loss. Investing in a reliable CSPM tool is a wise decision for any company that relies on cloud technology.
Final words
As the cloud computing security landscape evolves, so must cloud security architects. All companies need to be proactive in addressing their data vulnerabilities.
Advanced security tools such as Prevasio make protecting cloud environments easier. Having firm security policies avoids unnecessary financial and reputational risk. This combination of strict rules and effective tools is the best way to stay secure.
Rony Moshkovich
Rony Moshkovich, Director of Product for AlgoSec, has decades of practical research and engineering experience in the IT security industry. His background includes extensive management experience with an emphasis in software research and development, making him uniquely capable of guiding business requirements, and professional services for Enterprise, SMB, and consumer solutions.