





Operation “Red Kangaroo”: Industry’s first dynamic analysis of 4M public Docker container images


Linux containers aren’t new. In fact, this technology was invented 20 years ago.
In 2013, Docker entered the scene and revolutionized Linux containers by offering an easy-to-use command line interface (CLI), an engine, and a registry server. Combined, these technologies have concealed all the complexity of building and running containers, by offering one common industry standard. As a result, Docker’s popularity has sky-rocketed, rivalling Virtual Machines, and transforming the industry.
In order to locate and share Docker container images, Docker is offering a service called Docker Hub. Its main feature, repositories, allows the development community to push (upload) and pull (download) container images.
With Docker Hub, anyone in the world can download and execute any public image, as if it was a standalone application.
Today, Docker Hub accounts over 4 million public Docker container images.
With 8 billion pulls (downloads) in January 2020 and growing, its annualized image pulls should top 100 billion this year.
For comparison, Google Play has 2.7M Android apps in its store, with a download rate of 84 billion downloads a year.
How many container images currently hosted at Docker Hub are malicious or potentially harmful? What sort of damage can they inflict?
What if a Docker container image downloaded and executed malware at runtime? Is there a reliable way to tell that?
What if a compromised Docker container image was downloaded by an unsuspecting customer and used as a parent image to build and then deploy a new container image into production, practically publishing an application with a backdoor built into it? Is there any way to stop that from happening?
At Prevasio, we asked ourselves these questions multiple times.
What we decided to do has never been done before.
The challenge
At Prevasio, we have built a dynamic analysis sandbox that uses the same principle as a conventional sandbox that ‘detonates’ malware in a safe environment. The only difference is that instead of ‘detonating’ an executable file, such as a Windows PE file or a Linux ELF binary, Prevasio Analyzer first pulls (downloads) an image from any container registry, and then ‘detonates’ it in its own virtual environment, outside the organization/customer infrastructure.
Using our solution, we then dynamically analyzed all 4 million container images hosted at Docker Hub.
In order to handle such a massive volume of images, Prevasio Analyzer was executed non-stop for a period of one month on 800 machines running in parallel.
The result of our dynamic scan reveals that:
- 51 percent of all containers had “critical” vulnerabilities, while 13 percent were classified as “high” and four percent as “moderate” vulnerabilities.
- Six thousand containers were riddled with cryptominers, hacking tools/pen testing frameworks, and backdoor trojans. While many cryptominers and hacking tools may not be malicious per se, they present a potentially unwanted issue to an enterprise.
- More than 400 container images (with nearly 600,000 pulls) of weaponized Windows malware crossing over into the world of Linux. This crossover is directly due to the proliferation of cross-platform code (e.g. GoLang,.NET Core and PowerShell Core).
Our analysis of malicious containers also shows that quite a few images contain a dynamic payload. That is, an image in its original form does not have a malicious binary. However, at runtime, it might be scripted to download a source of a coinminer, to then compile and execute it.
A dynamic analysis sandbox, such as Prevasio Analyzer, is the only solution that provides a behavioral analysis of Docker containers. It is built to reveal malicious intentions of Docker containers by executing them in its own virtual environment, revealing a full scope of their behavior.
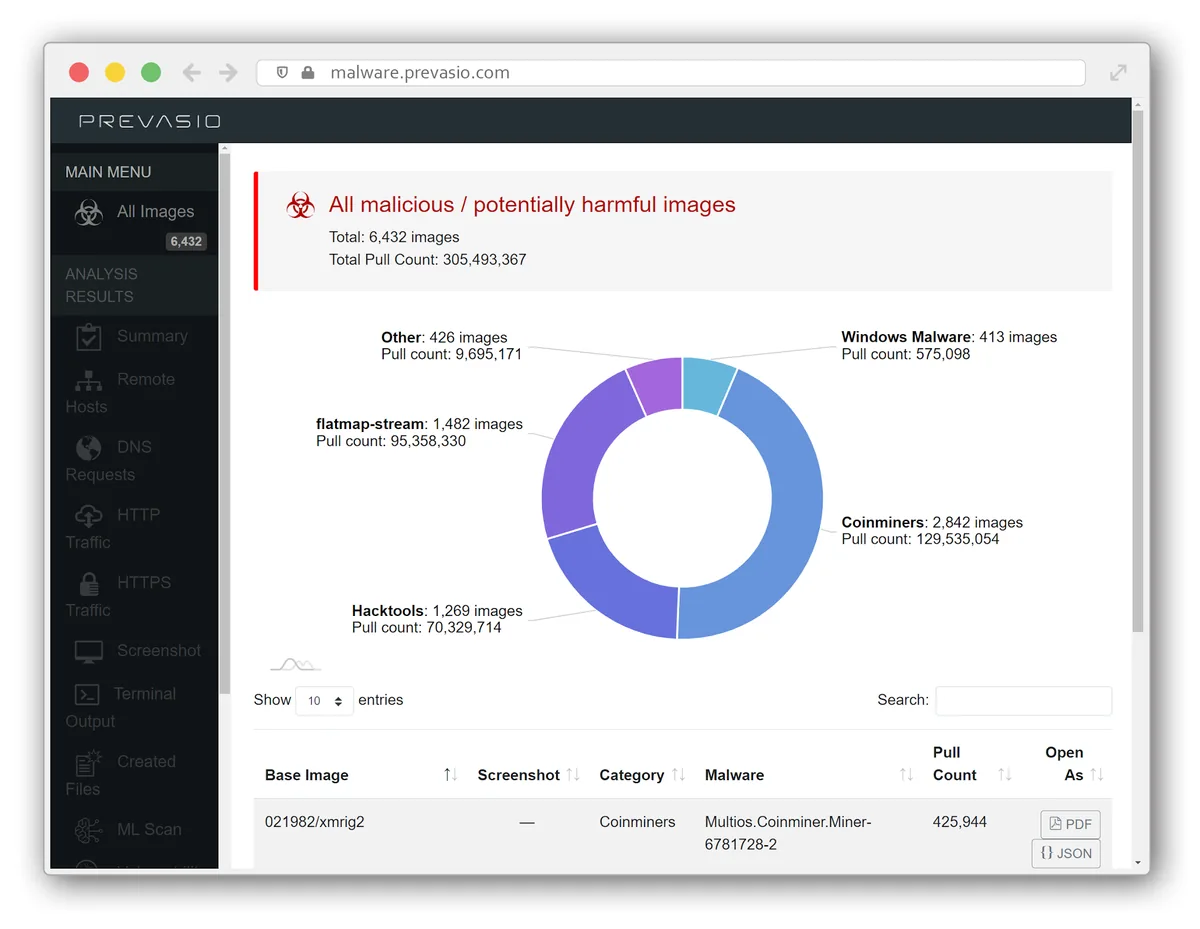
The whitepaper with our findings is available here.
Rony Moshkovich
Rony Moshkovich, Director of Product for AlgoSec, has decades of practical research and engineering experience in the IT security industry. His background includes extensive management experience with an emphasis in software research and development, making him uniquely capable of guiding business requirements, and professional services for Enterprise, SMB, and consumer solutions.